Why this matters
The three questions boards now ask about AI agents
68%
of security leaders see at least some unsanctioned use of AI and AI agents.
Okta Global CISO Insights 2026, 306 security leaders- 01
How many AI agents do we run, and where?
AI agents built outside IT, or left behind when their owner moves on, are the ones nobody can account for.
- 02
What can each AI agent connect to?
Every connector and data source an AI agent uses is a path to your data, sometimes with its author’s own access.
- 03
How is each AI agent governed?
Approval, applicable policy, review of actions and a retirement date, recorded for each AI agent.
What we connect to
Where we find your AI agents

CYBERWHITE
Read-only scan

Microsoft 365

Copilot Studio

Microsoft Azure

AWS

GitHub
We show exactly what we read on each platform during the scoping call. Talk to an expert
Not included: penetration testing, reading Copilot conversations, and platforms we do not connect to. AI agents on those platforms are recorded in your register from your team’s answers.
Product names and logos belong to their owners. Their use does not imply endorsement.
What we assess
Four things we check for every AI agent
Where each AI agent runs
Every AI agent across your connected platforms, recorded in one register.
What each AI agent can reach
Permissions, consents, admin roles and the data each AI agent can access.
Who owns each AI agent
An accountable owner and a business purpose for every AI agent.
How each AI agent is governed
Human approval, logging, testing and retirement, checked against the standards.
How the assessment works
Four steps, from first call to consultant review
Typically 2 to 3 weeks from the scoping call to the consultant review.
Deliverables
What you receive
AI agent register, listing every AI agent with its owner and business purpose
Shows which AI agents your organisation runs and who is accountable for each.
Findings for 53 controls, each with its evidence
Provides your auditor with evidence drawn from your own environment.
Remediation plan, with step-by-step guidance and gaps listed first
Sets out the actions for your team, starting with confirmed gaps.
AI agent governance policy, drafted for your organisation
Establishes one approval process for every new AI agent before deployment.
Two-page board summary
Gives your board a clear position on AI agent risk.
Dashboard access, for your team
Allows your team to view the findings online.
Consultant review, with your leadership
Confirms priorities and next steps, with each finding explained.
Two ways to engage
Start with the assessment. Keep the register current with ongoing reviews.
Both are quoted after a 30-minute scoping call, once we know your platforms and the number of tenants in scope.
01
Assessment
One engagement, 2 to 3 weeks. Every AI agent found, assessed and reported to your leadership.
- Read-only scan of the platforms in scope, 31 automated checks
- One workshop for the 22 governance questions a scan cannot answer
- AI agent register, findings for 53 controls, remediation plan, governance policy, board summary
- Consultant review with your leadership, dashboard access for your team
Scoped per Microsoft tenant. Additional platforms and tenants are itemised on the quote.
02
Ongoing review
For organisations that have completed the assessment. Each quarter, a fresh scan and a short call so the register never goes stale.
- Quarterly re-scan with changes since the last scan called out
- Register updated: new AI agents, retired AI agents, changed access
- Progress on the remediation plan, updated board summary
- 30-minute call with a consultant each quarter
Quoted at the end of the assessment, once the register exists.
Assessment lead
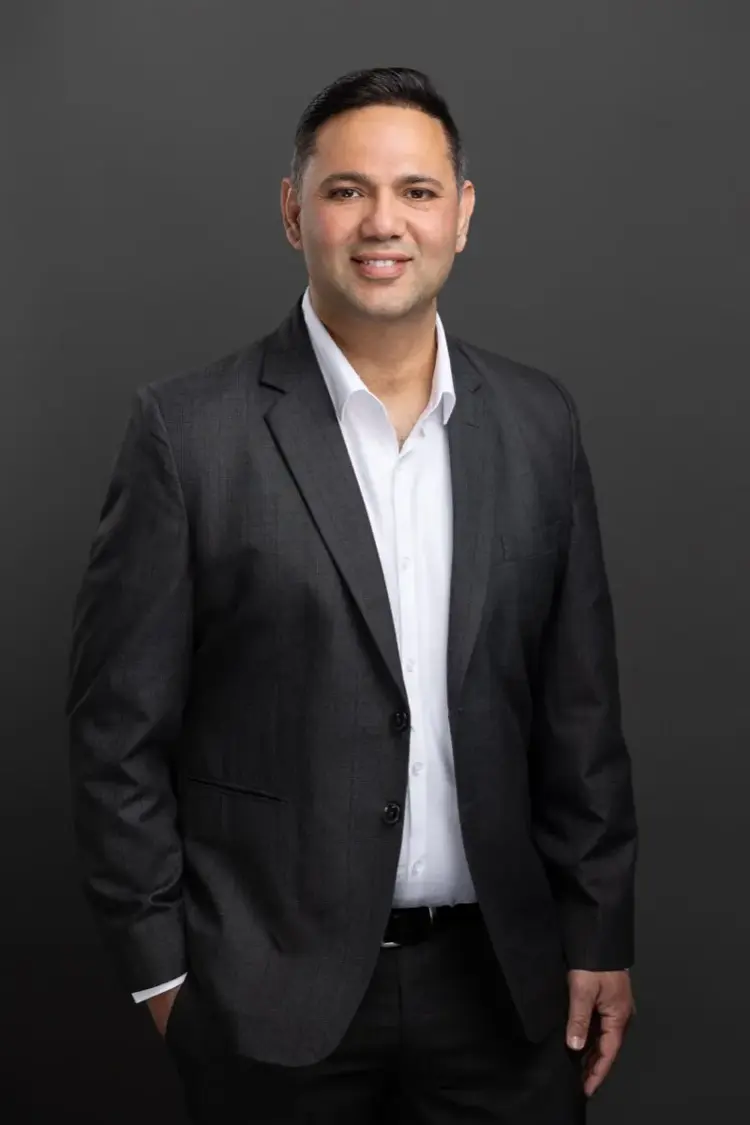
Pardeep Sharma
Founder and CEO, CYBERWHITE
- Lead AI Security Architect on large-scale Australian critical-infrastructure security.
- Two decades in infrastructure and enterprise architecture across banking, healthcare and government.
- Publishes on agentic AI risk, identity for AI agents and AI governance.
- Evidence from your own environment, not interviews alone.
- Every finding labelled: scanned, observed or reported.
- Australian owned. Data stored in Australia.
Mapped to ASD, NIST AI RMF and OWASP
- ASD Information Security Manual and agentic AI guidance
- NIST AI RMF, with its Generative AI Profile
- OWASP Top 10 for Agentic Applications
- OWASP Top 10 for LLM Applications
See how the controls map
| Control | Mapped to |
|---|---|
| Each AI agent has its own identity, separate from staff accounts. | OWASP ASI03ISM-2133 |
| An AI agent register is kept and regularly verified. | NIST AI RMF GOVERN 1.6NIST AI 600-1 GV-1.6-001ISM-2134 |
| The register records owner, purpose, identities, credentials and access for each AI agent. | NIST AI RMF GOVERN 1.6NIST AI 600-1 GV-1.6-003ISM-2135 |
| Application permissions held by apps and AI agents are the minimum needed. | NIST AI RMF MAP 4.2NIST AI 600-1 GV-6.1-007OWASP ASI03OWASP LLM06ISM-2156 |
| Tenant-wide delegated consents are the minimum needed. | NIST AI RMF MAP 4.2NIST AI 600-1 GV-6.1-007OWASP ASI03OWASP LLM06ISM-2157 |
| Content an AI agent retrieves is untrusted and cannot override its instructions. | NIST AI RMF MEASURE 2.7NIST AI 600-1 MS-2.7-007OWASP ASI01, ASI06OWASP LLM01ISM-2158 |
| A person approves before an AI agent takes a sensitive or high-impact action. | NIST AI RMF MAP 3.5, GOVERN 3.2NIST AI 600-1 MS-4.2-004OWASP ASI02, ASI08OWASP LLM06ISM-2113 |
| Every tool call, external request and output an AI agent makes is centrally logged. | NIST AI RMF MEASURE 2.4, MANAGE 4.1NIST AI 600-1 MS-2.6-005, MG-4.1-002ISM-2159 |
Questions
Is this a penetration test?
No. The assessment is not a penetration test. We review your AI agents and their governance using evidence from your own environment, and we do not attack them.
Will the assessment change anything in our environment?
No. The scan only reads. Your team makes every change in the remediation plan.
What does the assessment cost?
We send a quote after a 30-minute scoping call, before any work starts.
How long does the assessment take?
Typically 2 to 3 weeks from the scoping call to the consultant review. Your team attends one workshop and the review meeting.
We are outside Australia. Does the assessment still apply?
Yes. Your report can lead with NIST AI RMF or the OWASP Top 10 for Agentic Applications. Organisations in India and the European Union also receive regional notes.
Where is our data stored?
In Australia. Connection tokens are encrypted, and AWS access uses a read-only role you create, with no access keys.
Find out what your AI agents can reach.
Start with a 30-minute call.
CYBERWHITE designs its controls against published documents from ASD, NIST and OWASP. CYBERWHITE is not endorsed or certified by them.